
Somebody mentions a breach in a Wednesday meeting. You nod, say nothing, and ten minutes later you’re typing cybersecurity news today reuters into a search bar under the table. (Hypothetical, sure, but I’d bet a decent lunch it’s how a lot of these searches start.) What comes back is a mess: different dates, different publishers, and a range of certainty that runs from “police confirmed” to “a guy on Telegram said so.” I want to sort that out, and I’ll toss in a few everyday security habits for after the reading is over.
A warning about “today.” I’m writing this on October 7, 2026. By the time you read it the news will have shifted, probably twice. Use the examples as practice for how to read, not as a live feed.
What a cybersecurity news today reuters search returns
Mostly wire stories. Reuters keeps its cyber reporting inside the technology desk, so a search for cybersecurity news today reuters brings up breaches, ransomware gangs, state-backed hacking, and the arrests, indictments, and bills that trail behind them. Written for a business audience. You’ll learn who did what and why anyone should care, and you’ll learn very little about indicators of compromise or which build number fixes the hole.
ThreatQuotient lists a Reuters feed in its marketplace and describes the coverage in roughly those terms: data breaches, ransomware, criminal crews, nation-state activity, with some longer investigative work on policy and business fallout. Matches what I see.
So here’s the split I use, and the rest of this piece leans on it. Reuters answers “what happened and who’s involved.” It does not answer “what do I patch before lunch.” Nearly every mistake I see people make with cybersecurity news today reuters comes from asking one kind of source to do the other kind’s job.
One more thing in its favor: wire copy is written for someone who has never heard of a CVE. When you need to forward something to a director, or your mother, that matters more than you’d think.
Finding Reuters’ Cyber Coverage Fast
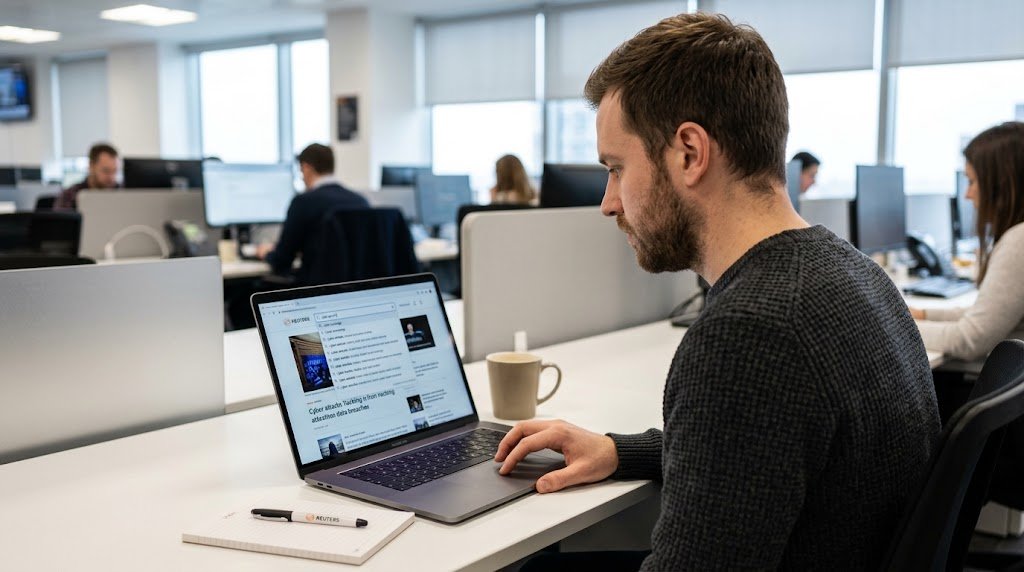
If you read cybersecurity news today reuters regularly, bookmark the cybersecurity section of Reuters’ technology pages. I couldn’t load that page while researching, so click it yourself and confirm it still works. The site search handles named groups and companies fine, and tacking on a month and year pushes old stories down.
Bylines help. The Dutch arrest story I’ll get to below carried two names, Raphael Satter and Anthony Deutsch, and reporters on this beat tend to stay on it for years, so a name you recognize is a search term you can reuse. Handy when you track cybersecurity news today reuters stories over months.
Tangent, because I tripped over it: Reuters copy travels. Fortune hosts a whole author page of it. I found one Reuters story only in a Spanish translation on a third-party site, which was fine for my purposes and also a small trap, since the date on a syndicated copy can differ from the original and translations lag. Check the dateline before you quote any cybersecurity news today reuters item. Every time.
Alerts: I believe Reuters killed its public RSS feeds years back, but I’m not sure, so verify before you build anything on one. For cybersecurity news today reuters alerts, newsletters and app notifications are the safer bet. And one small annoyance. Searching the exact phrase also drags in aggregator pages that borrowed the wording for traffic, so glance at the domain before you click.
Reuters vs Trade Sites, Side by Side
These are my generalizations, not measurements, and any given story will break the pattern.
| Source type | Where it shines | Where it falls short | Reach for it when |
| Reuters (news agency) | Context, named officials, legal and policy angles, plain language | Light on technical detail; picky about which incidents get covered | You need significance, or you’re briefing someone non-technical |
| Security trade sites (The Hacker News, SecurityWeek, Infosecurity Magazine) | Fast technical write-ups, CVE numbers, indicators | Uneven depth; some stories repeat one original source | You need specifics on a flaw or malware family |
| Independent investigators (Krebs on Security) | Deep reporting on individual actors | Slower, story by story | You want the backstory on a group or person |
| Government and vendor advisories (CISA, vendor bulletins) | Authoritative patch and exploitation status | Dry, and no context | You’re deciding what to fix |
| Weekly roundups | Many items in one sitting | Secondhand by design | You missed a week |
If I could keep one source on a bad day it would be the vendor advisory for whatever I run, not Reuters. But Reuters is what I’d hand a director who asks what happened. Different jobs, and that’s why cybersecurity news today reuters earns a slot in a daily mix without being the whole mix.
A Snapshot From October 7, 2026
Everything in this section came from trade outlets and weekly roundups, not Reuters, unless I say otherwise, so none of it counts as cybersecurity news today reuters coverage by default. I’m including it to show what a normal news day looks like. Every item is date-sensitive.
Police had a good week. Trade coverage says authorities seized the leak site and core servers of the KillSec ransomware group, and Europol tied the operation to roughly 1,000 suspected attacks. A 16-year-old in Spain was arrested on suspicion of running the thing.
Patching was less cheerful. Citrix shipped fixes for a NetScaler flaw tracked as CVE-2026-88779, scored 8.7 and exploited in targeted zero-day attacks. One weekly roundup also listed a Cisco SD-WAN Manager zero-day that hands attackers admin access, a SharePoint bug that slid into active exploitation, and an OpenSSL fix for a DTLS flaw that can leak heap memory.
Policy and breach news rounded it out. SecurityWeek reported that the U.S. Senate passed a bipartisan bill meant to strengthen healthcare cybersecurity, citing more than 730 breaches that touched over 270 million Americans last year. Cybernews reported a Denmark breach said to have exposed 8.8 million people.
Now look at what’s missing. As far as I can tell not every one of those items made it into cybersecurity news today reuters results, and that isn’t a defect. A wire service picks stories with a wide audience or a clear institutional angle. It’s not trying to catalog every CVE, and if you expect that you’ll walk away annoyed.
How One Story Gets Built
Definitions of “certainty” are useless. An example works better. On September 28, 2026, Reuters reporters in Amsterdam wrote that a Dutch man, widely covered in the media for going from cybercriminal to security professional, had been arrested in an investigation into the ShinyHunters hacking group. In the Spanish version I found, the Dutch police and his boss both spoke on the record, and the boss described Dutch forensic investigators visiting the office the night of the arrest. Reuters also said its attempts to reach the man, or to find a lawyer for him, hadn’t turned anything up yet.
Count the legs on that one. On-the-record sources, a named workplace, a visible effort to reach the subject. I’d trust the facts, with the standing rule that an arrest isn’t a conviction.
Then October 4. Reuters reported that a suspected ShinyHunters member who goes by “Rey” had reportedly been detained in Jordan, citing three people familiar with the matter. Trade sites picked it up. A few added a claim that he was now helping the FBI identify other members.
Same group, same week, totally different sourcing. For background on who Rey is alleged to be, Brian Krebs wrote a long profile of the admin back in November 2025. That kind of slow, single-subject digging is something a wire service rarely has room for.
Reading Anonymous Sourcing Without Panic
“Citing people familiar with the matter” shows up constantly in wire copy, including cybersecurity news today reuters stories, and by itself it isn’t a warning sign. Usually it means someone with direct knowledge spoke on condition of anonymity and the reporter decided they were credible. Three of them, as in the Jordan report, count for more than one.
Still not confirmation, though. Until an agency, a court, or the people involved say it on the record, I file the claim under “probably true” and keep it in its own mental drawer.
So who counts as a second source? Another outlet, but only if it did its own reporting. With the Jordan story, at least two sites I saw simply relayed “Reuters reported” and added background. That’s a courtesy, not a second confirmation. Five articles can trace back to one reporter.
If I could push one habit on anyone reading cybersecurity news today reuters or any other daily feed, it would be this: count independent sources, not headlines. Echoes feel like agreement. They aren’t.
Something else jumped out this week, though I wouldn’t build a theory on it. Teenagers sit on both sides of two unrelated stories: a 16-year-old suspected of running a ransomware crew, and a teenage alias tied to a data-extortion brand. Is that the field, or just what gets reported? No idea.
Attribution Stories Need Extra Care

Stories that name a country behind an attack are some of the most-read items in any week of cybersecurity news today reuters coverage, and they’re the ones I slow down on. This week’s trade sites carried a report that a China-aligned group tracked as TA419 ran credential-phishing campaigns against AI policy experts in the U.S. They also carried an item saying MI5 linked China’s Ministry of State Security to funding research involving more than 100 U.K.-connected academics. As far as I know neither is a Reuters story, but both show the shape.
Attribution comes in grades. Weakest: a vendor’s private view that some code or infrastructure resembles an older campaign. Stronger: a government statement naming an agency, which is what MI5 did. Strongest: a court filing, like the extradition of an alleged Iranian state hacker to the U.S. that SecurityWeek covered on October 2, where an indictment lays out specific charges.
Read state-backed stories in cybersecurity news today reuters results with that ladder in mind. “Linked to,” “consistent with,” and “assessed with moderate confidence” are all softer than “charged with.” Soft wording isn’t weakness. It’s accuracy, and headlines that sand it off annoy me more than almost anything else in this business.
Timing matters too. Governments sometimes time an attribution to a diplomatic moment, so the date can say as much about the announcer as the attack. I can’t prove that for any single case. Hold it loosely.
A Five-Step Cross-Check
Take a headline claiming a group stole data on federal employees. ShinyHunters made a claim like that about the FBI, so it’s a fair test case. For any cybersecurity news today reuters result carrying a big claim, here’s my order of operations.
Who’s speaking? The group, an agency, a researcher, or a reporter’s anonymous source. Next, is there a second voice that isn’t an echo, and if the agency hasn’t commented, write that down. Then compare the date of the claim with the date of the event, since extortion crews often announce a theft days or weeks after they got in. After that, look for detail somebody could disprove, such as a named vulnerability or a data sample. Vague claims are cheap. Specific ones are risky for whoever makes them. Last, wait. Not forever, only long enough for the first round of corrections.
That last step is the hard one. Breaking news pays people for speed, and most of us want to be the one who knew first. I think waiting an hour on a big claim almost never costs anything and often saves a retraction.
Is Reuters Fast Enough for Defenders?
For patching, no, and it was never meant to be. Wire coverage tends to arrive once a story crosses some threshold of significance, which can be well after a vendor posts an advisory. If a flaw in your firewall is being exploited right now, cybersecurity news today reuters won’t be where you hear it first. The advisory and the exploited-vulnerability lists will be.
CISA’s known exploited vulnerabilities catalog is the cleanest example. CISA calls it the authoritative list of vulnerabilities used in real attacks and suggests feeding it into your prioritization process. A listing there carries more weight for a patch queue than any headline I know of.
Go back to the Citrix item from the snapshot. A trade headline tells you a NetScaler flaw is being exploited. The vendor bulletin tells you which versions are hit and what to install. A wire story, if one shows up, tells you who got hit and whether governments are involved. Three sources, three jobs.
One personal rule for cybersecurity news today reuters stories and everything else: if my employer’s product is named in a headline, I stop reading and go find the advisory first. The article can wait ten minutes.
Turning Headlines Into Action Items
Reading cybersecurity news today reuters stories is the easy half. A headline matters only if it changes something you do, so after each scan I ask these in order:
- Do we run the product, service, or vendor named?
- Is the flaw already exploited, or only disclosed?
- Is there a fix, and did anyone test that it installs cleanly?
- Could stolen credentials or customer data reach us through a supplier?
- Who else needs to know, and in what words?
If the first answer is no, move on. Don’t feel bad about it. If it’s yes, the vendor advisory and the CISA catalog take over from the news story.
Small teams, I suspect, lose more time to the opposite problem: they read everything and act on nothing. A boring headline log with a “does this touch us” column beats a hundred open tabs. I’m guessing from how this usually goes rather than from data, so take that as opinion.
All of this belongs inside basic risk management, where you rank exposure by likelihood and damage and not by how loud the headline is. A breach at a vendor you’ve never used is background hum. A quiet advisory for a product you run in production is not.
Mistakes People Make With Daily Cyber News
Date blindness comes first. A search for cybersecurity news today reuters can float a story from last spring above this morning’s. Check the timestamp each time, and again on syndicated copies.
Second, claims treated as facts. ShinyHunters reportedly said it had stolen data on thousands of FBI employees, and trade sites repeated that widely. A group announcing a theft isn’t an agency confirming one, and extortion crews have every reason to inflate. When a headline says “hackers claim,” read the verb.
Third, raw counts with no context. The Senate bill coverage cited more than 270 million Americans affected by healthcare breaches in one year. That probably counts people several times over, since one person can sit in a dozen breaches. Good for scale. Bad as a population estimate.
Fourth, CVSS tunnel vision. An 8.7 that needs local access may matter less to you than a 6.5 on something facing the internet.
Fifth, forwarding a headline unread. Headlines are written to get clicked, and plenty promise more than paragraph three delivers.
AI Is Changing What Makes the News

Automated attacks have been creeping into headlines. SecurityWeek reported on October 2 that AI agents fired SQL injection attacks at U.S. and Canadian government sites, among them the U.S. Department of Education and Library and Archives Canada, and that researchers tied some of the agents to OpenAI. Microsoft separately warned, per Infosecurity Magazine, that AI is squeezing the time between first compromise and real damage down to minutes. I only have summaries of both, so I’d read them cautiously. Together they point somewhere, though.
What does that mean for anyone following cybersecurity news today reuters stories? Mostly that speed stories will get common, and “it happened fast” will stop being remarkable alone. Better questions: did defenders have a window, and was the weakness old?
It also changes how I weigh any single story. If attackers can grind through weaknesses at machine speed, the useful lesson in most headlines isn’t the novelty of the attack but the dull failure underneath: an unpatched box, a reused password, a forgotten admin panel. Which is why the passkey advice further down sits comfortably beside the fancier news.
I’m not saying AI makes every incident worse. This week’s coverage just suggests the gap between disclosure and exploitation is shrinking, and your reading routine should assume it keeps shrinking.
Watching Vendors in the Headlines
Reuters has covered security companies as business stories for a long time, a side of cybersecurity news today reuters that technical readers often skip. Older examples include its reports on Tenable raising a big funding round and, separately, Tenable’s CEO stepping down. The angle is money and management, which complements the technical angle on trade sites.
That matters if you’re a customer. A funding round, a buyout, a leadership exit, an IPO filing: any of them can change support quality, pricing, or product direction, and none of it appears in a vulnerability bulletin.
When a vendor you rely on turns up in business-side news, I’d note the renewal date on your contract and check whether anything in the story could touch it. Learning about a merger from a press article three weeks before renewal is a surprise you can avoid.
And if you’re sizing up suppliers more broadly, a list of major security vendors gives you a map of who competes with whom, which helps when a headline mentions an acquisition and you need to know whether the buyer is a rival of your current tool.
A Ten-Minute Morning Routine
You don’t need a dashboard to keep up with cybersecurity news today reuters stories. You need something that survives a busy Thursday.
Mine would look like this. Two minutes on one wire source, such as Reuters’ cyber section, for the big stuff. Three on one trade site for technical detail. Two on the exploited-vulnerability catalog and your vendors’ advisory pages. The last three go to writing a single line about anything that touches your systems.
That’s the whole thing. No endless feeds, no seventeen newsletters.
A search for cybersecurity news today reuters can be one doorway, but I’d rather bookmark the section than lean on a query, since queries drift toward whatever has the best search optimization.
Two warnings, both plain common sense. Skip cyber news right before bed if you ruminate. And don’t open links in “breaking news” emails, because attackers happily imitate headlines. Go to the site yourself.
Passing News to Non-Technical Colleagues

Translating is harder than reading. A paragraph about a SAML outage means nothing to an accounts team, and a paragraph about a teenage extortion ring means something dramatic and not much else.
I’d write three sentences: what happened, whether it affects us, what I’d like you to do. If the third sentence is “nothing,” say that plainly, because people stop reading messages that never tell them what to do.
Wire stories help here, including cybersecurity news today reuters items, since they’re already in plain language. A forwarded link plus your three sentences beats a pasted technical bulletin.
Over time, news becomes raw material for awareness training. A real incident from this week beats a stock slide. Infosecurity Magazine reported UK police urging passkey adoption after a reported 417 percent annual rise in account-takeover-driven cybercrime revenue. I’d treat that number cautiously, but the point about reused passwords lands well in a staff session.
Keep examples short. Don’t name individual employees. End each with one concrete habit.
If You Want to Work in This Field
Reading cybersecurity news today reuters stories daily is a quiet form of training. After a few months you notice patterns: which flaws get exploited fast, which groups recycle tactics, which vendors patch slowly. Interviewers pick up on a candidate who can talk about last week’s incident with some nuance.
For anyone aiming at the job, the analyst role is a common first target. The Bureau of Labor Statistics projects 21 percent growth in information security analyst employment from 2025 to 2035, with a 2025 median pay of $129,180. Those are all-analyst figures and new hires usually start below the median, so don’t read them as an offer.
My stance: news literacy matters less than hands-on practice and more than most people credit. Reading a headline critically is a skill you can build for free, ten minutes at a time.
FAQs
Where can I find cybersecurity news today from Reuters?
Use the cybersecurity section within Reuters’ technology coverage, or search a named group or company with a month and year, so your cybersecurity news today reuters search lands on current pages, and check the dateline on any syndicated copy.
Is Reuters reliable for cybersecurity news today?
Reuters is a major news agency with named bylines and a visible sourcing standard, but stories built on anonymous sources deserve extra caution until officials confirm them on the record.
How is Reuters different from trade security sites?
Reuters leans toward context, legal angles, and plain language, while trade sites publish faster technical detail such as CVE numbers and indicators of compromise, which is why cybersecurity news today reuters results work best beside them.
How often is cybersecurity news today from Reuters updated?
As far as I can tell, Reuters publishes as stories develop rather than on a fixed daily schedule, so check the site’s timestamps instead of assuming a morning digest.
What should I do after reading a breach story?
Check whether you use the named vendor, read that vendor’s advisory, look the flaw up in the exploited-vulnerability catalog, and tell colleagues in plain language whether it affects you.
Final Thoughts
If I squeezed this whole article into one sentence it would be: a headline is where reading starts and where action doesn’t. Everything else hangs off that. What you find under cybersecurity news today reuters gives you context, named sources, and a plain-language account of why something matters. It doesn’t give you patch instructions, and it was never built to.
The short version of the takeaways. Learn which job each kind of source does. Count independent sources instead of headlines, because echoes imitate agreement. Pay attention to how a story is sourced, since on-the-record officials and anonymous sources carry different weight. Check dates every time, particularly on syndicated pages. And turn each relevant story into one concrete step, even when that step is “no action needed.”
I’ll admit a bias. I distrust any news habit that feels productive but never changes a decision. Reading is cheap and feels like work, which makes it easy to confuse with the work itself. If a week of reading produces no ticket, no patch, and no message to a colleague, that’s worth noticing, and it usually means your sources aren’t matched to what you actually run.
My perspective, for what it’s worth, is that daily news habits matter more than people admit and less than they fear. You won’t stop a breach by reading faster. You can avoid being the last person in the building to hear about a flaw in something you run, and you can avoid repeating a shaky claim in a meeting because it showed up in five places that all trace back to one.
I also suspect the volume of stories keeps growing, with automated attacks arriving faster than most teams can read about them. That makes selection more important than speed. A short, steady routine will serve you better than chasing every alert, and one wire source plus one trade site plus your own vendor advisories is plenty for most people.
If you’re building that routine this week, keep it small. Bookmark the section you’ll really open, pick one technical source, add the advisory pages for your own tools, and set a ten-minute timer. Write down what you learn from the first few mornings. After a couple of weeks you’ll know which source earns its place, which one you can drop, and how much of your cybersecurity news today reuters searching was just noise.
An IT career coach with 7 years of experience helping beginners map out certification paths that actually lead to interviews, not just another resume line. He’s guided dozens of career-switchers through their first AWS or CompTIA exam and writes for itechnova.io, covering IT certifications, cybersecurity, and the software tools people actually need to know.
1 thought on “Cybersecurity News Today Reuters Readers Often Misread”