
Picture this. A mid-size logistics company gets an email from a vendor asking to update banking details for an upcoming invoice. Looks normal. Same logo, same tone, even references a real project name. Someone in accounts payable updates the record, sends the next payment. Three weeks later the real vendor calls asking why they haven’t been paid.
Not a hypothetical, by the way. A friend who runs IT for a regional distributor told me almost this exact story last year. And the fix wasn’t some elaborate new tool — it was a cybersecurity risk management process that simply didn’t exist before the incident happened. No verification step. No second approver. Nobody had ever sat down and mapped out what could go wrong with a routine payment change, because nobody had thought to ask.
That gap shows up more often than people assume. It’s part of why cybersecurity risk management stopped being a conversation reserved for banks and hospitals a while back. Any organization holding customer data, processing payments, running on a network hooked to the internet — which is basically everyone now — needs some version of this, whether they’ve formalized it or not.
What This Term Actually Means
Strip away the jargon and cybersecurity risk management is just a structured way of answering three questions: what could go wrong, how bad would it be, what are you doing about it. That’s the whole thing at its core, even though consultants love dressing it up with frameworks and acronyms until it sounds more complicated than it is.
It’s different from general IT security in one important way. Security is implementing controls — firewalls, patching, access limits. Cybersecurity risk management sits a layer above that, deciding which controls actually matter based on what you’re protecting and what’s realistically threatening it. You can have great security tools and still have weak cybersecurity risk management, if nobody’s prioritizing based on real exposure.
I think this distinction gets lost a lot. Companies buy a stack of security software, feel covered, and never step back to ask whether they’ve actually assessed where their real risk sits. Tools without a process behind them are just expensive noise, honestly.
The Real Cost Of Getting It Wrong
Numbers help more than opinions here. According to IBM’s 2025 Cost of a Data Breach Report, the global average cost of a breach landed at $4.44 million — a 9% drop from the year before, the first decline in five years. Sounds like good news until you look at the U.S. number specifically: a record $10.22 million, roughly four times what a comparable breach costs in India.
Here’s the breakdown worth sitting with for a second:
| Metric | Figure (2025) |
| Global average breach cost | $4.44 million |
| U.S. average breach cost | $10.22 million |
| Healthcare sector average (highest of any industry) | $7.42 million |
| Ransomware/extortion average | $5.08 million |
| Phishing-caused breaches | 16% of all incidents |
| Average breach lifecycle (detect + contain) | 241 days |
That last row is the one that sticks with me. 241 days, on average, to identify and contain a breach. Not a rounding error. That’s most of a year with attackers potentially sitting inside systems, and it’s exactly the kind of gap structured cybersecurity risk management is supposed to close through earlier detection.
Healthcare staying the costliest sector for the 15th year running is worth flagging too — it shows how much industry context actually matters here. A hospital’s cybersecurity risk management priorities look nothing like a marketing agency’s, because the assets at risk (patient records versus campaign data) carry totally different regulatory weight and black-market value.
The NIST Framework, No Fluff
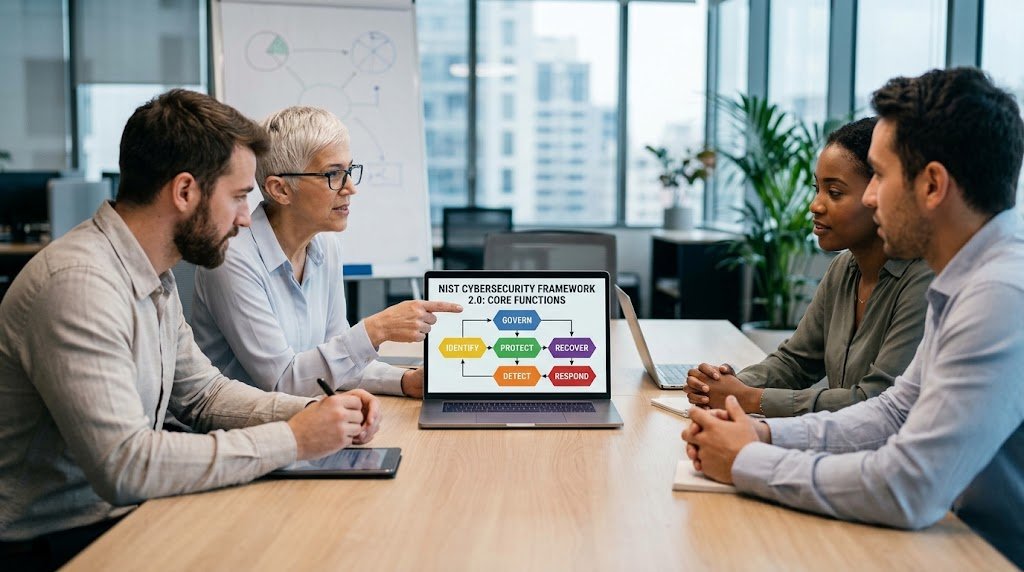
If you’re building or fixing a cybersecurity risk management program, you don’t need to invent your own structure from scratch. NIST published version 2.0 of its Cybersecurity Framework back in February 2024, and it’s become the reference point most organizations lean on now, even outside the U.S.
CSF 2.0 runs on six functions: Govern, Identify, Protect, Detect, Respond, Recover. Govern’s the newest addition, and honestly the biggest shift in the whole update. It puts leadership accountability at the center instead of treating cybersecurity as purely a technical department’s headache. Real philosophical change from the old five-function version.
Identify is where you inventory what needs protecting — systems, data, vendors, all of it. Protect covers the safeguards: access controls, training, data security. Detect and Respond are the operational muscle. Recover gets you back to normal after something breaks. Good cybersecurity risk management touches all six, not just the Detect and Respond parts that get the headlines and the budget.
What I like about CSF 2.0: it doesn’t hand you a rigid checklist. It links out to more detailed guidance instead, which means small businesses and massive enterprises can both use it without one side drowning in irrelevant requirements. If you want the source directly instead of someone’s interpretation of it, NIST’s own framework page lays out all six functions and their subcategories, no middleman.
Where Most Programs Break Down
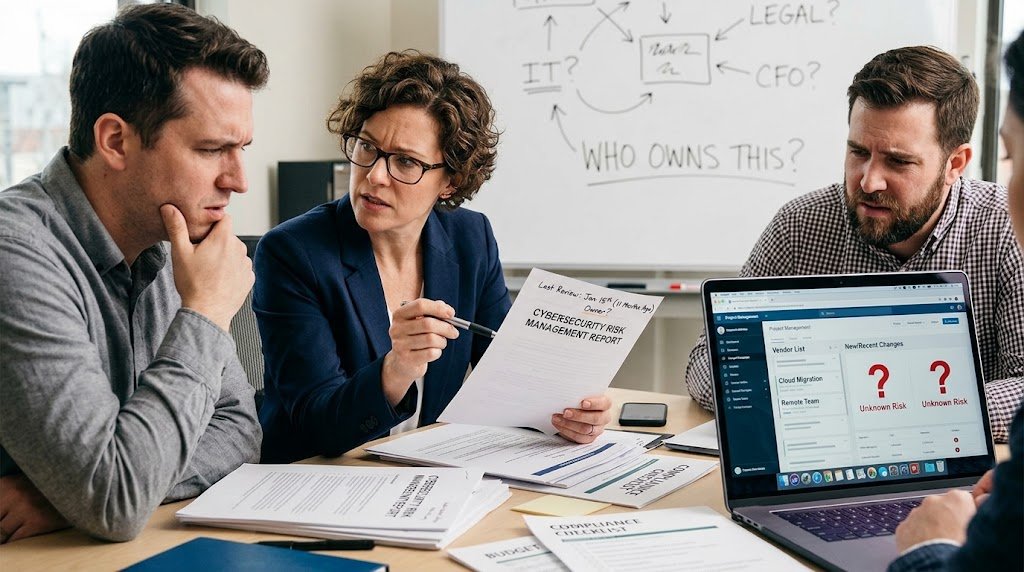
I’ll be blunt, because a lot of the advice out there is too polite about this. The biggest failure point in cybersecurity risk management isn’t a missing tool. It’s treating risk assessment like a once-a-year compliance box to check instead of a living process.
A company does a risk assessment in January, files the report, doesn’t touch it again until next January. Meanwhile they’ve onboarded three new vendors, migrated half their infrastructure to a new cloud provider, hired a remote team in a different country. None of that shows up in the risk register until the next scheduled review — which means the document’s been stale for eleven months out of twelve.
This is where outside eyes tend to help more than another internal meeting. A proper cybersecurity risk assessment run by people who aren’t emotionally attached to the existing setup usually surfaces blind spots internal reviews miss, simply because familiarity breeds assumptions nobody questions anymore.
Second break point: ownership. Ask five people at most mid-size companies who owns cybersecurity risk management and you’ll get five different answers — IT, legal, the CFO, “compliance,” or just a shrug. When nobody owns it clearly, nobody’s accountable when a gap gets found. And gaps just sit there.
A Risk Register People Actually Open
A risk register sounds bureaucratic, and at most companies, it is — a spreadsheet built once, buried in a shared drive, never touched again. That’s not what a working one looks like.
A functional risk register lists specific threats, not vague categories, rates likelihood and impact, assigns an owner, tracks mitigation status. It’s a living document, reviewed on a set cadence — not a compliance artifact pulled out once a year for the auditors. The gap between a good cybersecurity risk management program and a mediocre one often just comes down to whether this thing gets opened between audits.
Rating risk usually comes down to a simple matrix — likelihood on one axis, impact on the other. A phishing attempt against a low-privilege employee account sits in a different quadrant than a vulnerability in a system holding customer payment data, even though both technically count as “cybersecurity risks.” Treating them with equal urgency just wastes resources on the wrong fires.
I’d also push back a little on the instinct to make this list exhaustive. A 200-line risk register nobody reads is worse than a 20-line one reviewed monthly. Prioritization is the whole point. If everything’s rated critical, nothing actually is.
Third-Party Risk Is The Real Blind Spot
Here’s an observation from watching companies go through this over and over: most think about their own systems first and treat vendors as an afterthought. That’s backwards, statistically. IBM’s data shows vendor and supply chain breaches averaged $4.91 million — the second-costliest attack vector in the whole report.
Your cybersecurity risk management program is only as strong as the weakest vendor with access to your systems or data. A payroll processor. A cloud storage provider. A marketing platform with your customer list synced to it. Each one’s an extension of your attack surface whether you think about it that way or not.
Vendor risk assessment doesn’t have to be adversarial, either. It’s completely reasonable to ask a vendor for their SOC 2 report, their incident response plan, evidence of recent penetration testing, before signing anything. Companies that skip this step usually don’t skip it out of laziness — they skip it because nobody assigned the task to anyone, which loops right back to that ownership problem from earlier.
If your organization’s too small to build this internally, working with a firm offering managed cybersecurity services is a reasonable middle ground. You get structured vendor and internal risk monitoring without hiring a full security team from scratch.
How AI Is Rewriting The Math
Can’t write about this topic in 2026 without touching the AI angle, because it’s reshaping both sides at once. Attackers are using it. Defenders are using it. And the gap between organizations doing this well versus poorly is widening fast.
On the defense side, IBM found that organizations using AI and automation extensively saved an average of $1.9 million per breach compared to those that didn’t, mostly through faster detection and containment. That’s a real number — it suggests AI-assisted monitoring isn’t just a marketing buzzword, it’s measurably changing outcomes when it’s actually implemented well.
On the attack side, the same report found 16% of breaches involved attackers using AI, with phishing accounting for more than a third of those AI-powered attacks specifically. AI-generated phishing emails are noticeably harder to spot than the old broken-English scam messages, because the grammar’s clean now and the tone matches legitimate business communication convincingly.
There’s a third wrinkle worth naming: shadow AI, meaning employees using unapproved AI tools with zero oversight. The report found high levels of shadow AI added a real cost premium to breach totals, tied specifically to ungoverned tool use. That’s a governance gap, not a technology gap. It belongs squarely inside a cybersecurity risk management program, not off to the side as some separate IT policy nobody prioritizes.
How Often Should You Reassess?
No single universal answer, but “once a year” is almost always too thin for anything beyond the smallest, most static organizations. A reasonable baseline: full formal review annually, lighter check-ins quarterly, and ad hoc reassessment any time something major changes — new system, new vendor, an acquisition, real staff turnover in a sensitive role.
The trigger-based piece matters more than the calendar piece, honestly. Company adopts a new cloud platform in March? Waiting until next January’s scheduled review to assess what that decision introduced is asking for trouble. Good cybersecurity risk management treats significant operational changes as review triggers on their own, independent of whatever the calendar says.
Smaller companies sometimes figure this level of rigor is overkill for their size. I’d push back a bit there — a five-person company handling client financial data has real exposure regardless of headcount, and a lightweight quarterly review takes an afternoon, not a week. Scale the depth to your size. Don’t scale away the habit entirely.
Tools Versus Process
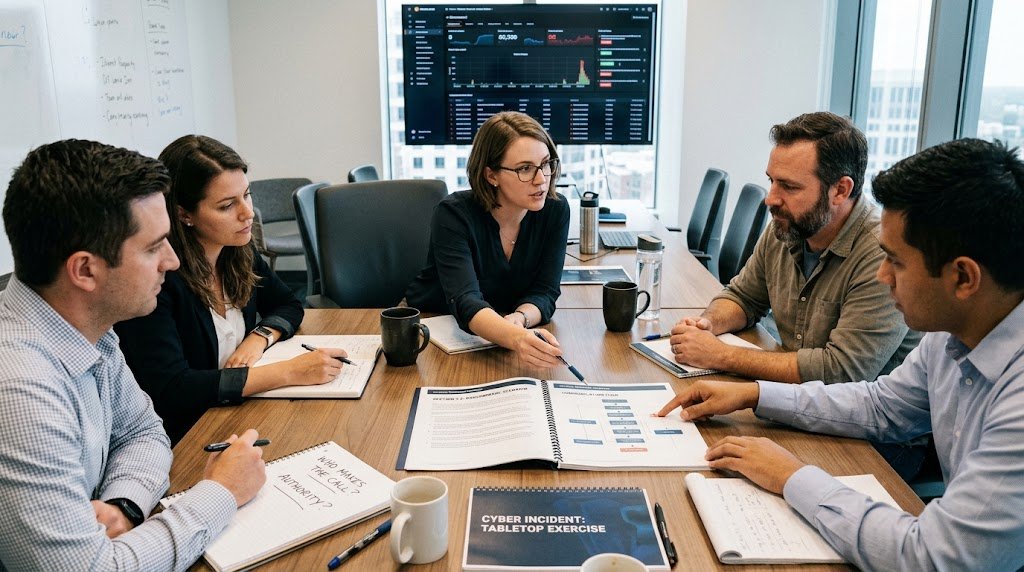
There’s an entire industry built around selling cybersecurity tools, and a lot of them are genuinely good. But I’ve watched companies spend six figures on software while skipping the unglamorous process work that would’ve prevented more incidents for a fraction of the price.
A well-run tabletop exercise — literally sitting a team down and walking through “what do we do if this exact scenario happens” — costs almost nothing and reveals gaps no software will ever catch. Who calls whom. Who has authority to shut a system down. Whether the incident response plan sitting in a shared drive is actually current, or was written three reorganizations ago and forgotten.
Not an argument against tools, to be clear. Decent cybersecurity software genuinely matters for detection speed and automated response, and given how fast AI-assisted attacks are accelerating, the gap between manual and automated monitoring keeps widening. But tools without process are basically a fire extinguisher nobody in the building knows the location of.
A Client Story: What Good Looks Like

Worth giving one concrete counter-example, since most of this piece has been about what goes wrong. A regional healthcare billing company I know of restructured its entire cybersecurity risk management approach after a near-miss with a ransomware attempt that got caught before encryption even started.
What changed wasn’t a massive tool purchase. It was ownership. They named one person accountable for the risk register, tied to specific KPIs reviewed quarterly by leadership — not buried in an IT status update nobody actually reads. They also brought in outside cybersecurity consulting services for an annual independent review, specifically so internal blind spots wouldn’t just get quietly re-confirmed year after year by the same people who created them in the first place.
Eighteen months later, their next audit turned up a noticeably lower number of unmitigated high-severity findings compared to the year before the restructuring. Nothing flashy about it. Just consistent ownership, a real review cadence, and treating cybersecurity risk management as an ongoing discipline rather than a document dusted off once a year for show.
Mistakes I See Over And Over
A few patterns repeat across nearly every organization I’ve looked at closely. Worth naming plainly instead of dancing around them.
Treating cybersecurity risk management as purely IT’s problem — when the biggest risks (vendor contracts, employee training gaps, executive email compromise) usually sit outside IT’s direct control entirely.
Skipping employee training because it feels like a checkbox exercise instead of a real defense layer. Given that phishing’s still the single most common attack vector, cybersecurity awareness training is one of the cheapest, highest-leverage investments available — and it gets deprioritized constantly in favor of flashier technical spending.
Assuming smaller size means lower risk. It doesn’t. Smaller companies often have fewer defenses and get used as a stepping stone into larger partners’ networks through vendor access.
Not testing the incident response plan until an actual incident forces the test. A plan that’s never been rehearsed falls apart under real pressure, gaps and all, exactly when you can least afford it.
Frequently Asked Questions
What is cybersecurity risk management in simple terms?
It’s the structured process of identifying what could go wrong with your systems and data, assessing how severe each risk is, and deciding what controls or actions address the highest-priority threats first.
How much does a data breach actually cost?
The global average sat at $4.44 million in 2025, with U.S. breaches averaging a record $10.22 million and healthcare breaches averaging $7.42 million, according to IBM’s 2025 Cost of a Data Breach Report.
What framework should a small business use?
NIST’s Cybersecurity Framework 2.0 works well across company sizes since it doesn’t prescribe rigid implementation steps, just six core functions — Govern, Identify, Protect, Detect, Respond, Recover — that scale to your resources.
How often should a cybersecurity risk assessment happen?
A full formal review annually is a reasonable baseline, with lighter quarterly check-ins and additional reviews triggered by major changes like new vendors, new systems, or significant staff turnover.
Is third-party vendor risk really that significant?
Yes — vendor and supply chain breaches averaged $4.91 million per incident in 2025, making it the second-costliest attack vector tracked in IBM’s report, right behind malicious insider incidents.
Final Thoughts
If there’s one thing I’d want someone to take from all this: cybersecurity risk management isn’t primarily a technology problem. It’s an ownership and discipline problem wearing a technology costume. The companies that handle this well aren’t necessarily the ones with the biggest security budgets. They’re the ones who’ve assigned clear accountability, review their exposure on a real cadence instead of a calendar formality, and treat vendors as part of their own attack surface instead of someone else’s problem to worry about.
The numbers back this up. A 241-day average breach lifecycle. Vendor incidents averaging nearly $5 million. AI now working for both attackers and defenders at the same time. None of that gets solved by buying one more piece of software. It gets solved by building a process that actually gets used, reviewed, updated when things change — not filed away until next year’s audit forces someone to open it again.
I’ll be honest about where I land here: most organizations already have enough tools. What they’re missing is the unglamorous, ongoing discipline of actually managing what those tools are protecting against, and keeping that picture updated as the business changes shape underneath it. Less exciting to write about than a new AI-powered detection platform, sure. But it’s the part that actually moves outcomes.
If you’re reading this because something already went sideways, start with ownership before you go shopping for more software — name one person accountable for the risk register today, not next quarter. And if nothing’s gone wrong yet, that’s exactly the moment to build the process, while you still have the luxury of doing it calmly instead of scrambling through a crisis.
An IT career coach with 7 years of experience helping beginners map out certification paths that actually lead to interviews, not just another resume line. He’s guided dozens of career-switchers through their first AWS or CompTIA exam and writes for itechnova.io, covering IT certifications, cybersecurity, and the software tools people actually need to know.
1 thought on “Cybersecurity Risk Management: 7 Costly Mistakes”